TecnoArtesanos Tech BlogTecnoArtesanos Tech Blog

Blog

0
Sergio Morales
Wednesday, 09 April 2025 / Published in Uncategorized

Microsoft: Windows CLFS Vulnerability Could Lead to ‘Widespread Deployment and Detonation of Ransomware’

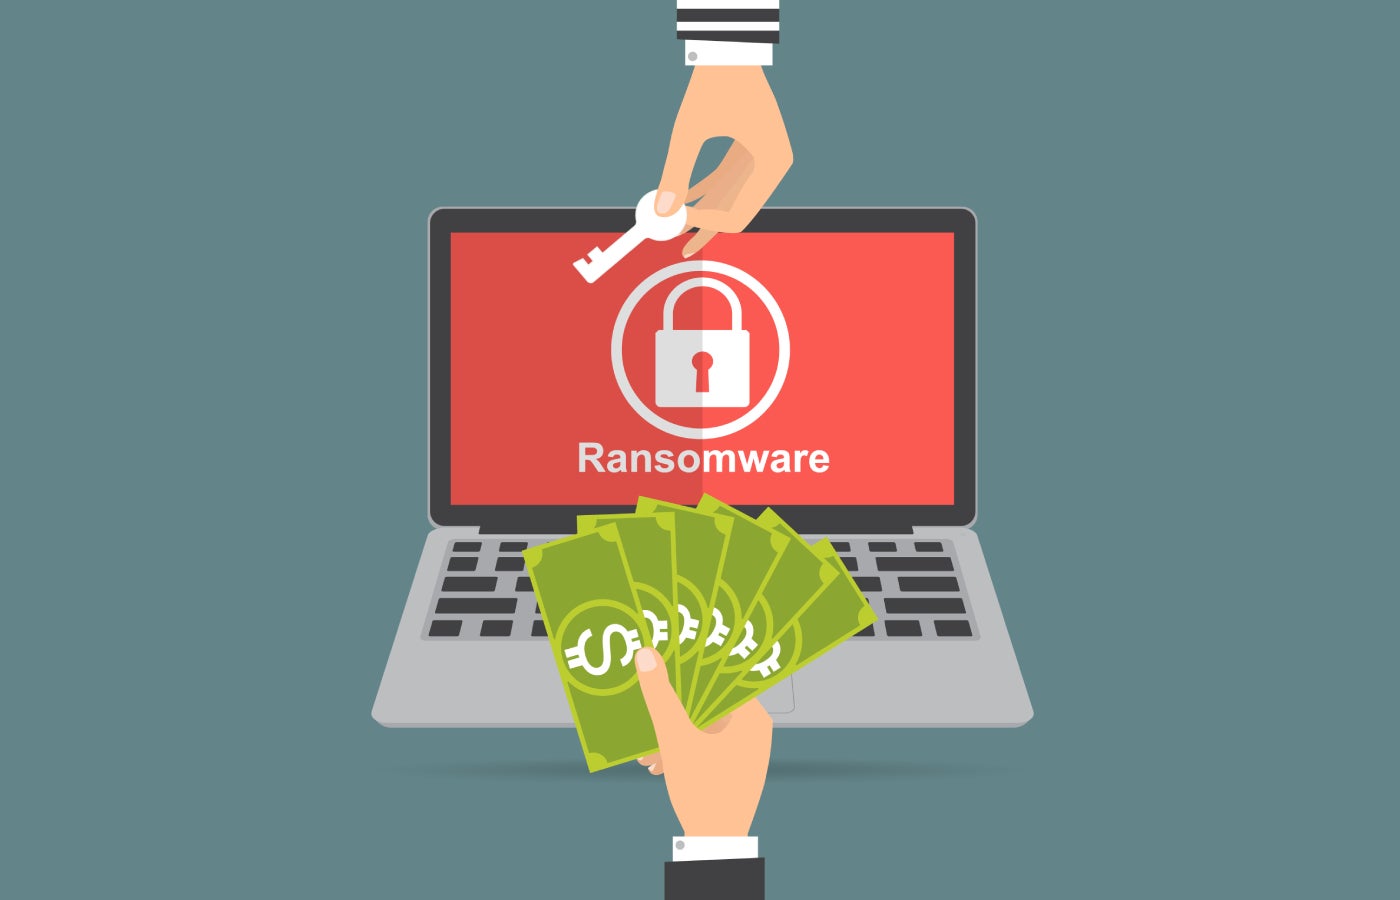
Flat vector illustration of a hand holding money for paying the key from hacker for unlock folder.
Image: nicescene/Adobe Stock

Microsoft has detected a zero-day vulnerability in the Windows Common Log File System (CLFS) being exploited in the wild to deploy ransomware. Target industries include IT, real estate, finance, software, and retail, with companies based in the US, Spain, Venezuela, and Saudi Arabia.

Contents
  • Who is behind the exploitation?
  • Windows 10, Windows 11, and Windows Server are vulnerable
    • Must-read security coverage
  • How exploitation works

The vulnerability, tracked as CVE-2025-29824 and rated “important,” is present in the CLFS kernel driver. It allows an attacker who already has standard user access to a system to escalate their local privileges. The individual can then use their privileged access for “widespread deployment and detonation of ransomware within an environment,” according to a blog post by the Microsoft Threat Intelligence Center.

The CFLS driver is a key element of Windows used to write transaction logs, and its misuse could let an attacker gain SYSTEM privileges. From there, they could steal data or install backdoors. Microsoft often uncovers privilege escalation flaws in CFLS, the last one being patched in December.

Patrocinado por TecnoArtesanos ¿Tu empresa ya está usando IA? Automatizamos procesos, integramos asistentes inteligentes y conectamos tus sistemas. Descubre cómo →

In instances of CVE-2025-29824 exploitation observed by Microsoft, the so-called “PipeMagic” malware was deployed before the attackers could exploit the vulnerability to escalate their privileges. PipeMagic gives attackers remote control over a system and lets them run commands or install more malicious tools.

SEE: TechRepublic Exclusive: New Ransomware Attacks are Getting More Personal as Hackers ‘Apply Psychological Pressure’

Who is behind the exploitation?

Microsoft has identified Storm-2460 as the threat actor exploiting this vulnerability with PipeMagic and ransomware, linking it to the RansomEXX group.

Once known as Defray777, the attackers came onto the scene in 2018. They have since targeted high-profile organisations such as the Texas Department of Transportation, the Brazilian government, and Taiwanese hardware manufacturer GIGABYTE. The group has been linked to Russian nationals.

The US’s cyber agency has added the 7.8-rated vulnerability to its Known Exploited Vulnerabilities list, meaning that federal civilian agencies are required to apply the patch by April 29.

Windows 10, Windows 11, and Windows Server are vulnerable

On April 8, security updates were released to patch the vulnerability in Windows 11, Windows Server 2022, and Windows Server 2019. Windows 10 x64-based and 32-bit systems are still awaiting fixes, but Redmond says they will be released “as soon as possible,” and “customers will be notified via a revision to this CVE information” as soon as they are.

Devices running Windows 11 version 24H2 or newer cannot be exploited this way, even if the vulnerability exists. Access to the required system information is restricted to users with the “SeDebugPrivilege” permission, a level of access typically unavailable to standard users.

Must-read security coverage

How exploitation works

Microsoft observed threat actors using the certutil command-line utility to download a malicious MSBuild file onto the victim’s system.

This file, which carried an encrypted PipeMagic payload, was available on a once-legitimate third-party website that had been compromised to host the threat actor’s malware. One domain PipeMagic communicated to was aaaaabbbbbbb.eastus.cloudapp.azure[.]com, which has now been disabled.

Once PipeMagic was decrypted and run in memory, the attackers used a dllhost.exe process to leak kernel addresses, or memory locations, to user mode. They overwrote the process’s token, which defines what the process is allowed to do, with the value 0xFFFFFFFF, granting it full privileges and allowing the attackers to inject code into SYSTEM-level processes.

Next, they injected a payload into the SYSTEM winlogon.exe process, which subsequently injected the Sysinternals procdump.exe tool into another dllhost.exe process and executed it. This enabled the threat actor to dump the memory of LSASS, a process that contains user credentials.

Following credential theft, ransomware was deployed. Microsoft observed files being encrypted, a random extension added, and a ransom note named !_READ_ME_REXX2_!.txt dropped on affected systems.

¿Quieres aplicar esto en tu empresa?

En TecnoArtesanos desarrollamos software, integramos IA y creamos experiencias digitales para negocios que quieren crecer.

Conversemos Nuestros servicios

¿Te gustó este artículo? Síguenos en Facebook para más contenido como este.

What you can read next

OpenAI prepara agentes de IA especializados de hasta 20,000 dólares para ser rentable en 2029
Musk activa Starlink en Irán, pero los problemas de internet continúan
OpenAI considera comprar Chrome para optimizar a ChatGPT, si Google es forzada a venderlo

Tecnología hecha a mano para tu negocio

Software, IA, sitios web y diseño. Hablemos de tu proyecto.

¿Hablamos? Síguenos en Facebook →

Recent Posts

  • ¿Hasta qué punto el consumo de agua de la IA se vuelve un problema?
  • En las redes sociales, guardar silencio hace ruido
  • Cómo Medellín está usando IA para resolver el “caos operativo” de su industria textil
  • Tech bros, machos alfa y utopías digitales: Paulina Borsook ya había visto la película en que vivimos
  • Este es el primer agente de IA al que realmente estoy dispuesta a delegar mis datos

Recent Comments

  1. A WordPress Commenter on Welcome to My Tech Blog – A New Chapter in Innovation

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025
  • April 2025
  • March 2025
  • February 2025
  • August 2016

Categories

  • Uncategorized

Recent Posts

  • ¿Hasta qué punto el consumo de agua de la IA se vuelve un problema?

    “Protejan nuestra agua”, “Agua para las persona...
  • En las redes sociales, guardar silencio hace ruido

    Me he pasado las últimas semanas desplazándome ...
  • Cómo Medellín está usando IA para resolver el “caos operativo” de su industria textil

    Mucho antes de que Medellín fuera reconocida po...
  • Tech bros, machos alfa y utopías digitales: Paulina Borsook ya había visto la película en que vivimos

    Borsook no tiene ninguna duda de que el disparo...
  • Este es el primer agente de IA al que realmente estoy dispuesta a delegar mis datos

    Una de las primeras cosas que hice al dejar mi ...

Archives

  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • November 2025
  • October 2025
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • May 2025
  • April 2025
  • March 2025
  • February 2025
  • August 2016

Categories

  • Uncategorized
TOP
TecnoArtesanos

Un estudio boutique que crea experiencias digitales: desarrollo de software, inteligencia artificial y soluciones en la nube, con el cuidado de la joyería fina.

¿Hablamos?

Servicios

  • Desarrollo de software
  • Integración de IA
  • Experiencias digitales
  • Redes sociales y diseño

TecnoArtesanos

  • Inicio
  • Portafolio
  • Nosotros
  • Blog

Contacto

  • +506 8730-7941
  • [email protected]
  • WhatsApp
  • Facebook
© 2026 TecnoArtesanos. Todos los derechos reservados. tecnoartesanos.com
TecnoArtesanos — Software a la medida, IA y sitios web para tu negocio. Conoce nuestros servicios →
✦ TecnoArtesanos

¿Te interesa llevar esto a tu negocio?

Escribimos sobre tecnología porque la construimos. Si tienes un proyecto en mente, conversemos: la primera llamada no tiene costo.

  • Desarrollo de software a la medida
  • Integración de inteligencia artificial
  • Sitios web y experiencias digitales
  • Redes sociales y diseño gráfico
¿Hablamos? Ver servicios

¿Prefieres WhatsApp? +506 8730-7941 · Síguenos en Facebook